Container Security stories
Joint users of Kubernetes can now move from finding vulnerabilities to hardening container images faster as the gap to exploitation narrows.
Rising use of AI coding tools is widening software supply-chain risks for businesses across the Middle East, Türkiye and Africa.
Security teams can now track newly disclosed CVEs in live systems, as RapidFort expands its supply chain tools into production monitoring.
The update aims to cut remediation costs and stop teams wasting time by re-analysing vulnerabilities without enough business context.
Supply chain compromises helped actively exploited flaws to 215 in the first half of 2026, as attackers used trusted tools and platforms to steal credentials.
Joint customers can now see RapidFort's remediation guidance inside Wiz, helping them triage container CVEs without changing scanning workflows.
It widens Broadcom's support model beyond Spring, giving customers verified fixes for Java, Python, Node.js and data services as vulnerabilities surge.
Enterprise users should gain tighter control over AI agents, as SAP and NVIDIA link runtime isolation with business authorisation and audit trails.
Teams running AI agents at scale could save idle compute and tighten isolation as Google opens Agent Substrate on Kubernetes Engine.
Australian firms could face faster breaches as model-driven attackers shrink exploit times to hours, making containment and zero trust vital.
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
Customers will get human-verified open source fixes as Broadcom expands Spring security coverage and counters risks from AI-generated patches.
The experimental setup lets AI teams run untrusted model code in isolated Ray clusters on Google Kubernetes Engine without exposing host containers.
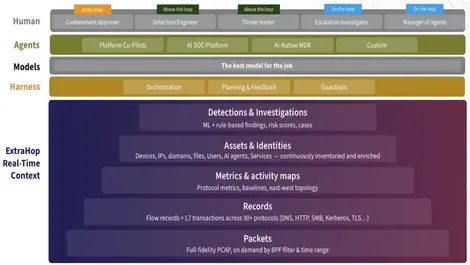
Security teams face wider blind spots as ExtraHop's new sensor brings full inspection of 400 Gbps data centre traffic to RevealX.
Growing use by major tech groups is helping open source secrets manager OpenBao win trust as cloud and AI credential risks mount.
Researchers can claim up to USD $1 million for breaking Vercel Sandbox's isolation, as the cloud provider opens its boundary to public scrutiny.
The accreditation strengthens Adfinis's hand with customers seeking secure open source tools for hybrid cloud systems and digital sovereignty.
The preview could help GKE users enforce cluster-wide security without clashing with namespace rules, especially in multi-tenant environments.
Security teams could spot newly disclosed flaws within minutes as rising CVE volumes and faster attacks squeeze response windows.
Private cloud operators may cut hardware costs by a third as Broadcom folds AI-assisted threat prevention and API security into VMware tools.